How a scan works#
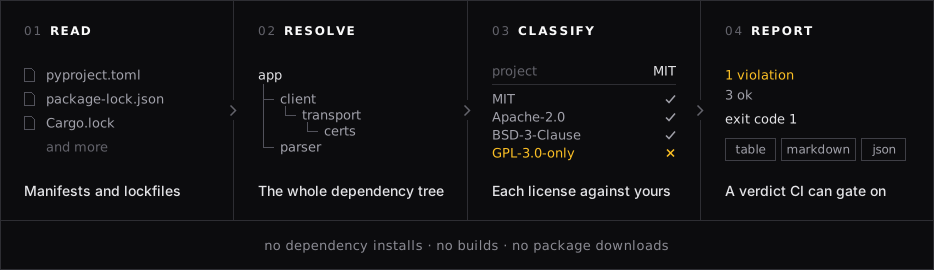
- Read. licenseal finds the manifests and lockfiles under the scanned directory: see What is scanned. The files it reads are listed for each ecosystem. It runs no package manager.
- Resolve. A lockfile gives the dependency tree as it is installed. Where no lockfile covers a dependency, licenseal walks the registry and marks the versions it picks as estimates. See Dependency resolution and Versions and estimates. A dependency that comes from a git repository, a URL, or a path is an off-registry dependency.
- Classify. A package's license is read from public registry metadata, or from
composer.lockfor a locked PHP package. It is read as a license expression, given a risk level, and compared with the project license. See How licenseal decides. - Report. The result is a table, a Markdown file, or JSON, and an exit code that CI can gate on. See What fails a check.
Nothing is installed or built, and no package archive is downloaded. Every host that is contacted is listed under Network egress, and what is sent to it under What leaves the process.